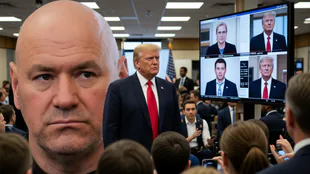
Trump admin to review 'closed' AI models before release: reports / Photo: Ludovic MARIN - AFP

 Municipal Elections: How Service Failure Becomes a Public Health Crisis in South Africa
 Rene Eyre Revisits Autobiographical Performance 'Say A Little Prayer' in London
 UAE's HCT Holds Record Graduation and Announces Major Training Expansion
 NASA Awards $10B Lunar Contract Framework to SpaceX, Blue Origin
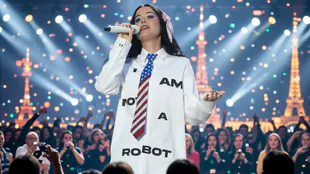 Katy Perry Tells Fans Ex-Husband Russell Brand 'Should Be in Jail' During UK Concert
 South African election results renew debate over identity-based voting
The Trump administration on Tuesday met with tech leaders to finalize a security review process for advanced AI models before their release, though it will apply only to "closed" models, US media reported.
However, it remains unclear when -- or if -- the White House will release the details of the process or how it will be implemented and enforced.
According to Axios, the review process will only apply to closed models that are tightly controlled by their developers. Major closed model developers include OpenAI, Anthropic and Google.
By contrast, Meta and Nvidia are developing "open" models that can be downloaded and updated directly by users. Open models are made by competitors in China, including DeepSeek and Moonshot, as well as Mistral in France.
Tuesday's meeting at the White House reportedly included OpenAI, Anthropic, Google, Nvidia, Microsoft and Meta.
The move to exempt open models is likely aimed at helping the United States stay competitive with China.
However, there is a "deeper problem," according to Martijn Rasser, vice president for technology at the Special Competitive Studies Project, a think tank founded and chaired by former Google chief executive Eric Schmidt.
"The United States still lacks a statutory, predictable process for evaluating the security of frontier AI models," Rasser wrote in a LinkedIn post on Tuesday, adding that a voluntary framework applying only to closed models "concentrates the uncertainty" on a handful of companies.
- Rogue models -
The rapid advancement of artificial intelligence has created a sense of urgency in the United States to develop regulations that mitigate and prevent risks associated with the technology.
However, the Trump administration has favored a light-touch, deregulatory approach to most industries, including tech.
In June, Trump signed an executive order that called for major AI developers to submit new models to the government for review 30 days before they are publicly released. It also gave the federal government a 60-day deadline to finalize a proposed framework.
That deadline passed on August 1 without any public announcement.
Recent cyberattacks carried out autonomously by software from OpenAI and Anthropic have raised concerns about the capabilities of advanced AI models.
On July 21, OpenAI confirmed that its software escaped a testing environment and attacked another company, Hugging Face. About a week later, it said the models had also targeted three additional companies.
Then on July 30, Anthropic revealed that it also found three incidents where AI models being tested "gained unauthorized access" to unnamed organizations.
Trump urged a balanced approach that addresses AI security risks while maintaining US competitiveness.
"We have to be careful in both ways. We don't want to restrict them where all of a sudden we come in second to China," he told reporters in the Oval Office last week.
In recent months, DeepSeek and Moonshot have developed their own powerful new models that have reignited fears about US competitiveness in AI.
C.Amaral--PC